Post-Quantum Security
Post-quantum cryptography across the telecom stack
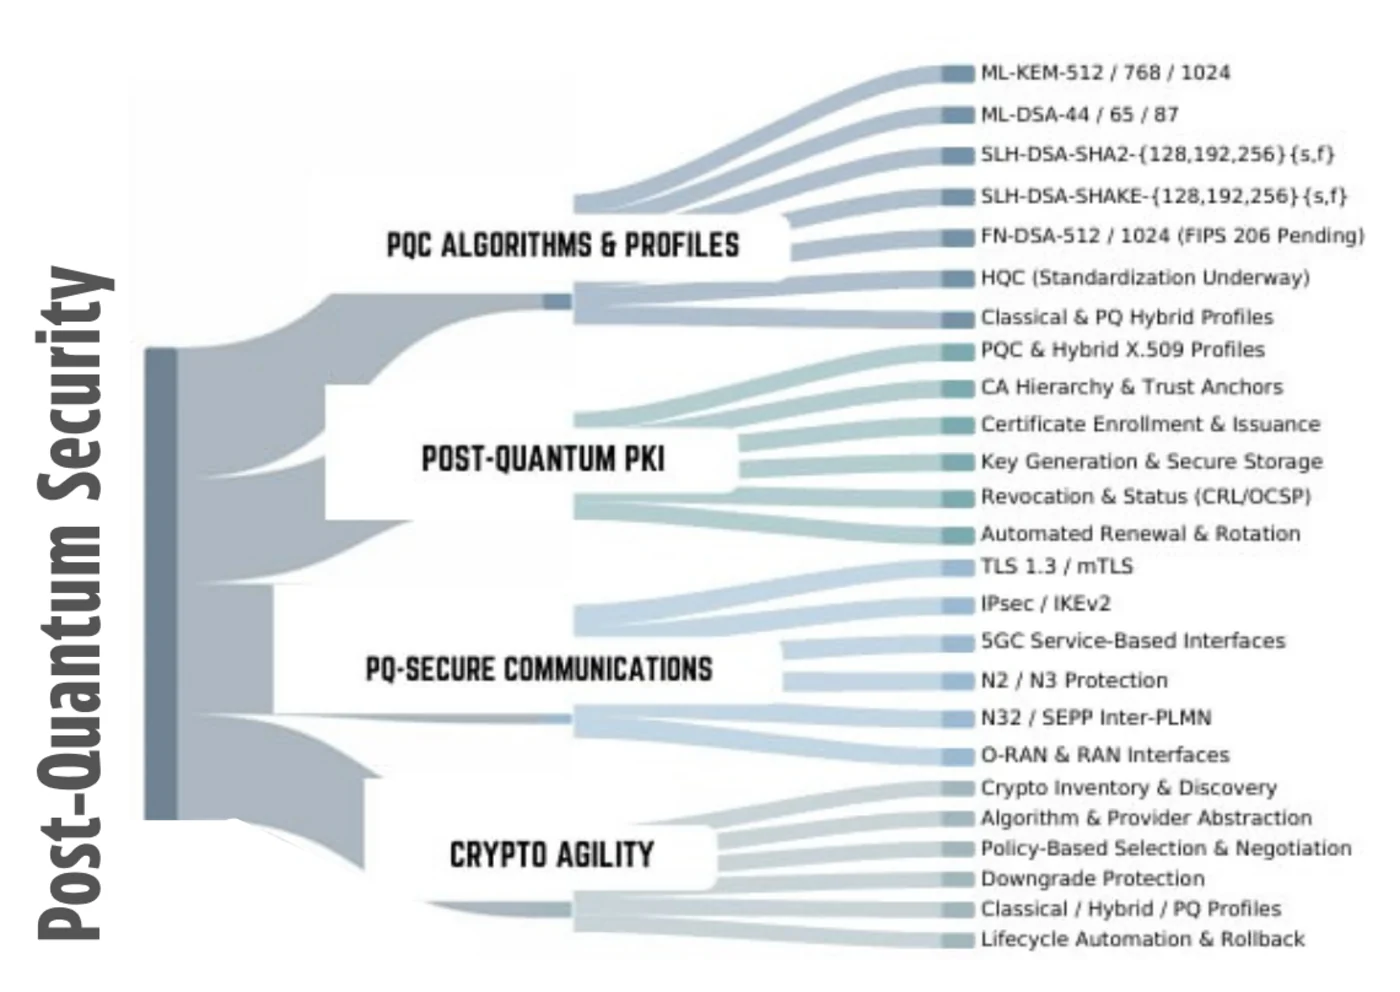
6G infrastructure being designed today may remain operational for decades. Security therefore needs to consider not only today's threats, but also the long-term impact of quantum computing. Open6GE integrates post-quantum security across the telecom architecture.
An important principle here is crypto agility. Networks should not be tied permanently to one algorithm. They need the ability to discover deployed cryptography, select policies, migrate between classical, hybrid and post-quantum profiles, manage certificates and keys, and prevent cryptographic downgrade. That capability will be critical for any long-lived 6G infrastructure.
In practice this reaches the service based interface inside the 5G core, the N2 and N3 reference points, roaming security through N32 and the SEPP, and the PKI that issues and rotates the certificates underneath all of it.
Related
Related areas
Identity for AI Agents
Identity and authorization for network agents
Verifiable identity and controlled authority for agents acting on RAN, Core, SMO and infrastructure.
Read more →CNTC, Cloud-Native Telecom Certification
Automated conformance testing and certification
Telecom and cloud requirements turned into automated tests, measurable evidence and auditable results.
Read more →